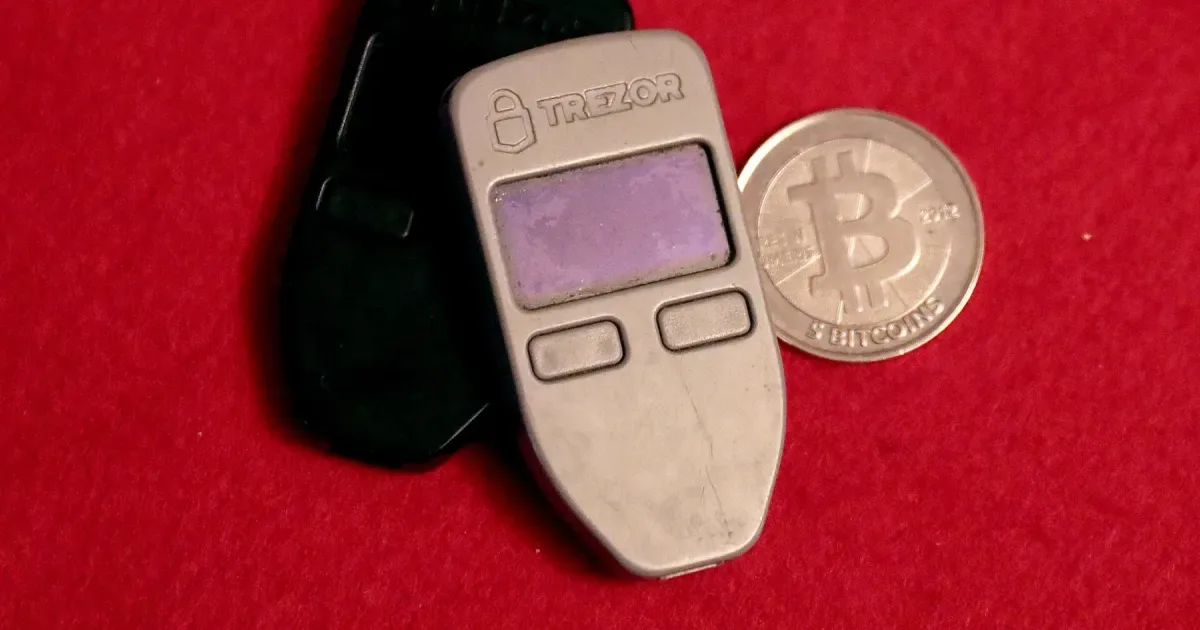
Update, October 7, 2026 Coinkite's status page now covers more than this August 4 report named: Mk2 and Mk3 before firmware 4.2.0, Mk4 and Mk5 standard releases before 5.6.0, and Q before 1.5.0Q. It also says a passphrase does not repair an affected seed. The sections below that mention Mk3 only or a protective passphrase are superseded. Check the status page before you decide.
Attackers have stolen about 1,816 BTC, roughly $116 million, from more than 5,200 Coldcard hardware wallet addresses since July 30, according to Fortune's August 3 count. They rebuilt the keys offline, using a 2021 firmware bug that made some seed phrases guessable. Coinkite, the maker, has shipped patched firmware and tells affected owners to move funds now.
The first wave hit on July 30. Galaxy Research clocked it at 41 minutes: about 1,083 BTC, worth $70 million, swept from 1,196 addresses in one automated run, The Hacker News reported. A second wave followed on July 31, a third over the weekend and a fourth on Monday morning. Galaxy had counted 1,367 BTC after the first three.
The attack was still unfolding when Coinkite, the Canadian company behind Coldcard, published an open letter telling affected users to move their coins immediately. Its founders called the stretch, in their words, "some of the hardest in this company's history."
A bug that skipped the hardware chip
The flaw traces to a March 2021 firmware build for the Coldcard Mk3, versions 4.0.1 through 4.1.9 and some earlier releases, BleepingComputer reported. When a device generated a new wallet, a bug sent the process through a software random number generator. The hardware chip that was meant to supply the entropy, the randomness a seed is built from, was bypassed.
Seeds from the flawed generator looked like normal 12 or 24 word seed phrases and behaved like them. Their pool was small enough to search, so the keys were weak from the day they were created. That weakness stayed dormant for five years.
Whoever ran the sweep had prepared. Every theft transaction used the same hardcoded fee of 30 satoshis per virtual byte and left no change output, the signature of an automated tool. Chainalysis found the attacker took the richest wallets first: about $30 million in the first ten minutes and $1.8 million from a single victim.
Coinkite disclosed the flaw publicly about 30 hours after the first wave and shipped patched firmware by August 1. Benzinga reported that it also halted shipments of affected stock. None of these steps returns a stolen coin.
What Coldcard owners should do
Exposure depends on where the seed was created. A seed generated on a Mk3 running the 2021 firmware is the danger case. Coinkite's guidance is to assume it is compromised and move everything to a fresh seed on patched firmware or a different device.
Users who supplied their own entropy with dice rolls were described as protected at the time. We originally wrote that a strong BIP-39 passphrase also gave real protection. Coinkite's status page now says otherwise: a strong, unique passphrase adds a barrier but does not repair a seed generated on affected firmware, and only seeds built from 50 or more independent dice rolls may be exempt from migration. When the cost of being wrong is everything, owners should move rather than weigh probabilities.
Mk3 on 2021 firmware, 4.0.1 to 4.1.9, is the risk case.
An affected seed can be rebuilt offline.
Use patched firmware or a new device, and add a passphrase.
Sweep to the new wallet. Never type the old seed online.
A scavenger phase usually follows an incident like this. Fake Coldcard checker sites, fake refund portals and urgent messages offering to help victims migrate are built to harvest the seed phrases the original attacker could not reach. The rule in our scam guide applies word for word: anyone who asks for a seed phrase is stealing, whatever the letterhead says.
What the exploit does and does not break
CoinDesk captured the debate within a day of the first wave: if cold storage can be drained, holding an ETF looks safer. We read it differently. The exploit is an argument against unaudited entropy, not against self-custody. The flaw was not in bitcoin, in the secure element or in the seed phrase standard. It was one firmware bug in one product line five years ago.
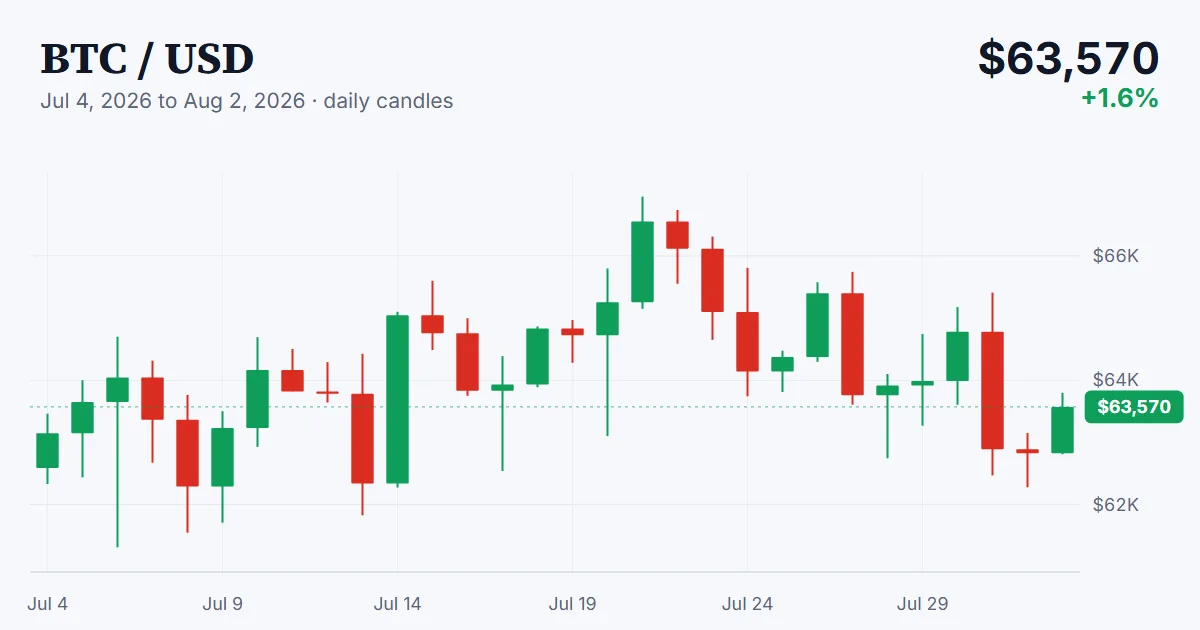
That is the class of risk that spreading funds across devices, adding a passphrase and following the basics in our wallet security guide are meant to contain. Bitcoin itself traded near $62,500 through the weekend, closer to its ETF flow worries than to the hack, and the coins moved with no protocol failure at all.
What broke was narrower and more personal: confidence in a device bought so that its owner would not have to think about this again.